- Check what your copilot changed. If a person still has to log in and click before any work happens, your product's execution model hasn't moved.
- Audit your product's actions and permissions next. Agents need those actions exposed as callable tools, with permissions scoped to each agent instead of a logged-in user's session.
- Map one workflow step by step before you commit to a rebuild. Mark which steps agents can run and which still need a person.
- Use that map to sequence the rebuild work. It protects the domain logic you already own and sets the foundation for outcome-based pricing when agents deliver measurable results.
Your AI assistant went live last year, and the launch went well. Plenty of customers tried it in the first few weeks, and then usage settled into the same small group of power users. Now your largest customer's procurement team is asking something the assistant can't answer: what can their agents do inside your product when nobody from their team is logged in?
That question is what an AI-first SaaS product has to answer, and it's arriving quickly. Gartner predicted in August 2025 that 40% of enterprise apps will integrate task-specific AI agents by the end of 2026, up from under 5% in 2025. If your product isn't one of them, your customers' agents will start working around it.
Agentic SaaS is the broad category. AI-first SaaS is what your product becomes when agents and events run its core workflows and people step in for the decisions. The usual advice for getting there is to bolt agents onto what you have or to start over. For an established product, SaaS modernization for agents sits between those two and is a smaller job than a rewrite, because most of what an agent needs is already in your codebase.
What Agentic SaaS Means (and Where Teams Get It Wrong)
Agentic SaaS often gets planned as a feature, the next roadmap item after the AI assistant. It's better understood as a change in who executes the work. In an AI-assisted product, the AI helps a person who is logged in and acting. In an AI-executed product, the agent does the acting inside limits your team sets, and a person reviews what it did.
That's why treating agentic SaaS as a feature tends to stall. One team can ship a feature without touching the rest of the product. Execution doesn't work that way, because the rest of the product assumes a human session behind every action. Permissions are checked against a user's role, and the audit trail records who clicked.
Gartner made a related point in 2025, warning that integrating agents into legacy systems is technically complex and often disrupts workflows. It recommended rethinking the workflows themselves. Rethinking a workflow is a different job from rewriting a codebase, and the rest of this guide shows how to do the first without the second. The architecture assumption changes first, and the features follow from it.
Agentic SaaS vs. AI Copilot: What Is the Difference?
A copilot lives inside the interface and helps whoever is already there. It can summarize a record or draft a reply, but someone still has to open the app and make each decision. An AI-first SaaS product changes who does the work. Agents start a workflow and carry it through, while a person sets the goal and steps in when something falls outside the rules.
monday.com has been open about going through this. According to a case study Anthropic published in August 2026, monday's teams spent May 2025 shipping AI features across the platform, and adoption was strong at first. Its VP of Product said the features helped people summarize and sort information, but they didn't create lasting usage. The company rebuilt its product experience around agents working alongside people and launched it in May 2026, and customers have had more than 5 million interactions with those agents since.
Gartner saw the same pattern across the market in 2025, warning that plenty of vendors were relabeling assistants and chatbots as agents. By its estimate, only about 130 of the thousands of companies selling agentic AI have the real thing.
A quick test shows which category your product sits in today. Ask if an AI feature can start and finish a task for a customer with nobody logged in. If every AI action needs a person to open a screen and trigger it, you have a copilot, whatever the release notes call it. That also tells you how much of your product still assumes a person at the screen.
What Happens to Your SaaS When AI Agents Become the Users?
Think about what your product expects from the person using it. They log in, find the right view, read the data, decide what it means and click the button that makes something happen. Your permission model, onboarding flows, usage analytics and seat-based pricing were all designed around that person sitting at that screen.
An agent has no use for any of the navigation. What it needs is a list of the actions it's allowed to take for a given customer, and a reliable record of what happened each time it took one.
The pricing implications of that shift are a separate problem. For your roadmap, the engineering side matters more: the changes your team has to make before an agent can do the work a user does today. The way to find where that work starts is to look at a single workflow.
What Is the Right Starting Point for an Agentic SaaS Redesign?
Pick one workflow your customers run every week and write down each step a person takes to get it done. An approval workflow usually goes something like this: log in, open the queue, inspect the record, check it against another system, click approve and let the requester know.
In an AI-first version of that same workflow, the system notices the condition, decides what to do, takes the action and tells the owner what happened. Nobody has to open anything to set it going.
With both versions written down, go back through the current one and mark who should own each step.
Once you've done this, you're no longer designing a screen. The logic that decides what approve means for this customer has been in your codebase for years. What you're missing is a way for something other than a logged-in person to call it.
You can probably already name the workflow your customers would hand to an agent first.
The harder part is seeing which parts of your codebase it touches, and which of those an agent could call today. A working session on that one workflow gives you:
- A step-by-step map of that workflow, marked by who should run each step
- A list of the product actions it depends on, including the ones with no callable interface yet
Talk Through One Workflow With an Engineer
What Needs to Become Agent-Accessible in Your SaaS?
With the agent's steps marked, the next job is listing what the agent has to reach to do them. In a product that's been in the market for a few years, nearly all of it exists already. It's just been wired to the interface.
Read down the right-hand column and you'll notice the gap is mostly about shape. You have the capabilities, and they're packaged for a person clicking through screens. Repackaging them is engineering work you can scope and estimate, and it's a lot smaller than rebuilding the logic underneath. Before you start, it helps to know how many agents will be calling them.
When Does Your SaaS Need a Multi-Agent Architecture?
Multi-agent SaaS comes later than it sounds. Start with one agent per workflow, because a single agent with a clear goal and a short list of tools is much easier to test and to permission.
You'll know it's time to split the work when one agent's responsibilities start pulling against each other. One part of the workflow might need write access to billing while another only reads tickets, and a single agent handling both ends up with far more access than either job needs. A step that needs a long, specialized context can also crowd out everything else the agent is holding.
monday.com's IT ticket handling is a live example of the split. One agent classifies and triages incoming tickets while a separate one detects incidents and opens a response, and each has its own job and its own permissions.
Every split adds coordination work, mostly around shared context and clean handoffs between agents. That coordination belongs in a shared layer of its own. However many agents you end up with, something still has to tell them when to start.
What Is Event-Driven SaaS, and Why Do Agents Need It?
Event-driven SaaS starts work when something happens in the business, without waiting for someone to open the app. A payment fails, a contract enters its renewal window, a ticket breaches its SLA or a shipment misses a scan. Your product is almost certainly recording those events already.
The trouble is what happens next. In a typical SaaS product, the event becomes a row in a table or a badge on a dashboard, and it waits there until someone happens to notice. In an AI-first product, the event kicks off the workflow itself. Business rules decide if it qualifies, and an agent handles the steps that need judgment before the downstream action goes out.
monday.com built its agents to take work this way. People hand tasks to an agent with triggers and mentions inside the platform, much as they'd assign something to a colleague.
Getting there is mostly plumbing. Your product needs an event stream that agents and other services can subscribe to, and its actions need to be idempotent so a retried event doesn't charge a customer twice. Once events are starting the work, the dashboard ends up with a different job.
What Does SaaS Look Like Without Dashboards?
Your product will still have dashboards. The difference is that a dashboard stops being the place every workflow has to begin.
For anything agents run, the screen becomes where a person goes when the system needs a decision or has flagged something unusual. The routine cases get handled without anyone visiting it.
monday.com's campaign workflow shows how this plays out. A strategist agent turns a marketer's rough notes into a structured brief, and a builder agent produces the landing page from it. Before a person sees anything, a reviewer agent checks the page against brand guidelines. By the time the marketing manager gets involved, there's one decision left: publish it or send it back.
That shifts where your design effort goes. The screens that matter most are now the exception and approval views, and they have to show what the agent did and why, with enough context that someone can decide at a glance.
All of this depends on agents being able to call your product's capabilities safely, and that's where most of the engineering sits.
How Do You Make Existing SaaS Features Agent-Executable?
Forrester's 2026 enterprise software predictions expect 30% of enterprise app vendors to launch their own MCP servers, which is how outside AI agents work directly with a vendor's platform. The server is a thin layer, and your customers' security teams will judge what sits behind it.
Expose Product Capabilities as Tools
Turn each action from your inventory into a tool with typed inputs and outputs and a description an agent can reason about. Wrap the service methods you already have, and start with the actions in the workflow you mapped.
Scope Permissions for Each Agent
An agent working for a customer should hold only the permissions its task needs, scoped to that customer's tenant. OWASP's 2025 Top 10 for LLM applications calls the failure here Excessive Agency, where an agent holds more functionality or permission than its task needs. Giving an agent a human admin's role is the quickest way there.
Make Every Agent Action Observable
Log every tool call with the agent, customer, inputs, result and the reasoning the agent recorded. Your support team will need it the first time a customer asks why something changed.
Define Safe Execution Limits
Give each tool rate limits and spend limits, and flag the actions that can be undone. The autonomy rules in the next section depend on it.
If your team keeps pushing this list to next quarter, you're reading the gap correctly.
The hard part is knowing which capabilities to wrap first, and which permission changes your current role model can take. A capability mapping session on one workflow gives you:
- The actions in that workflow that should become agent tools first
- The permission scopes each tool needs, checked against your current role model
- The points where your audit trail breaks when an agent acts
- A first-release sequence your team can put on the roadmap
Map One Workflow for Agent Execution
Which SaaS Workflows Should Run Autonomously?
Autonomy is something you set action by action. Gartner predicted in 2025 that over 40% of agentic AI projects will be canceled by the end of 2027, and weak risk controls are one of the reasons it gives. Deciding your boundaries before launch is how you keep your rollout out of that group.
Where Agents Act on Their Own
Low-value actions you can reverse, with a clear definition of success, can run without a gate. Categorizing a ticket or updating a status field are good examples. The agent acts and logs what it did, and someone reviews a sample afterward, which is what people mean by human-on-the-loop oversight.
Where Deterministic Logic Stays in Control
If your code already computes the right answer, as it does for tax calculation or entitlement checks, keep it as code. The agent can call it, and it never gets to reinterpret the result.
Where Humans Approve Exceptions
Anything that moves money or can't be undone waits for a person. The agent prepares the action along with its reasoning, and someone approves it in one step. That's human-in-the-loop, and you can relax it one action at a time once the logs show the agent is getting it right.
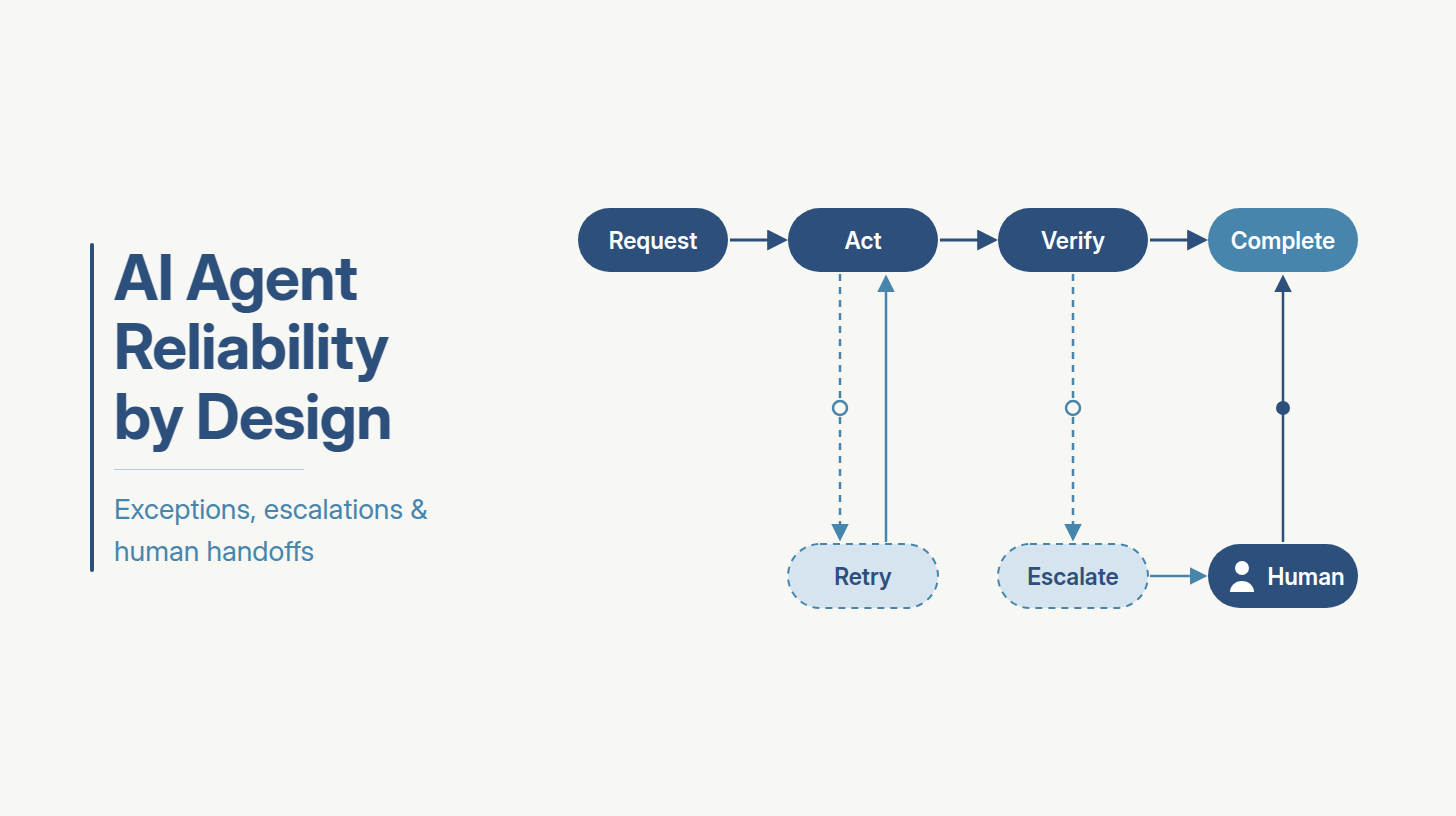
How agents behave once they're live in production is a separate engineering problem, and this piece on AI agent reliability covers it in depth. The boundaries themselves are enforced in your architecture, which is the next thing to look at.
What Architecture Sits Behind an Agent-Ready SaaS Product?
An agent-ready product runs on the same layers you have today. What changes is the kind of load each one carries.
Your APIs and event streams become the main way work enters the system, so they need the same uptime and versioning discipline your UI gets now. Agents also call in tight loops and retry when something fails, and that shows up in your rate limiting and your capacity planning.
Identity has to handle a new kind of actor. An agent working for a customer needs its own credentials and its own audit identity, kept separate from any person on that account.
Orchestration and observability are usually the layers you add. Something has to route events to the right agents and keep a record of every action they take across a workflow.
Data is the one that's easiest to underestimate. monday.com's team found that agents perform better when they work from live project data and structured workflows, and its backend had to hold up at enterprise scale. The company ended up investing in its own data layer, monday DB, alongside the agent work.
Written out like this, the list can make the job sound enormous. In practice, most of it is adapting what you already have.
Do You Need to Rewrite Your SaaS to Make It AI-First?
For an established product, no. A full rewrite throws away the parts agents depend on most, including years of domain logic, customer data, integrations, authentication and business rules your team has already debugged in production.
monday.com's rebuild is a good reference point here as well. The company rebuilt the product experience around agents, and it built those agents on the context, workflows, permissions and governance the platform already had. Building on what already works was one of the five lessons its team took from the transition.
Layers You Can Usually Keep
Domain logic and business rules stay, because they're the deterministic core your agents will call. Customer data and its history stay too, although you may need new ways to query them. Your existing integrations stay as well, and many of them become agent tools in their own right.
Layers That Usually Need Re-Engineering
The permission model tends to need the most work, since it was built around human roles. Your API layer has to cover complete actions an agent can call safely, and event handling has to start workflows as well as update records. The interface also needs exception and approval views for the work agents are now running.
Which of these comes first depends on the workflow you pick. That's why it makes sense to assess one workflow at a time and trace it through every layer it touches.
What Does the Agentic SaaS Execution Model Look Like in Practice?
To make this concrete, here's one workflow traced end to end. It's a hypothetical example built from the steps above, using failed-payment recovery in a B2B billing product, and it doesn't describe a client engagement.
It starts when a customer's card payment fails. A business rule checks the account and finds a three-year customer with no previous failures, so it qualifies for automated recovery. An agent looks at the account history to choose the retry timing, then drafts a message in the customer's language. Both the retry and the email go out through tools with scoped permissions.
If the retry fails twice, the workflow stops and a finance user gets an approval request showing what the agent tried. Whatever happens, the outcome shows up in a report the customer's finance lead reads every week. Nobody logged in to start any of this, and the only screen that came into play was the exception view.
That also changes what your customer is paying for, which is where AI SaaS transformation shows up on the invoice. Fin, Intercom's AI agent, charges $0.99 per outcome on its published pricing, with no seat fees when it runs on another vendor's helpdesk. Once your product is delivering outcomes, you can price on them, and the seat count stops being the figure that matters.
Taken together, the sections above add up to five changes.
What Does an AI-First SaaS Rebuild Require?
An AI-first SaaS rebuild changes five assumptions your product was originally built on.
Each row is an engineering change inside layers you already own, and you can order the changes by the workflows your customers care about most. What's left to decide is which workflow goes first and what it touches. That's the question an Ideas2IT assessment is designed to answer.
How Does Ideas2IT Assess Your SaaS for an AI-First Rebuild?
What the Assessment Covers
Ideas2IT does this work through Forward Deployed Engineers who join your product team from day one. They work in your codebase and sit in your standups, and they're measured on your engineers' OKRs. That matters here, because the permission model and tool layer are code your team owns after the engagement ends.
The assessment starts with Legacyleap, Ideas2IT's application modernization platform. Its Assessment and Comprehension modules read your codebase and dependencies and document the business logic under your screens. You get a written map of where each capability lives, which is what the keep-or-re-engineer call for each layer depends on.
When the workflow is ready for agents, the build runs on Agent Hero, an open-source agentic infrastructure layer Ideas2IT built. Your engineers start the tool and orchestration work on infrastructure the FDE team already knows.
What You Receive at the End
Ideas2IT holds SOC 2 Type II certification and the AWS AI Services Competency, formerly the Generative AI Services Competency. Both matter once the work touches customer tenant data.
After the first workflow is mapped, the same FDE team builds it with your engineers.
You have a workflow your biggest customers want an agent to run, and a product that still waits for someone to log in.
Before you commit budget, you need to know what that workflow touches in each layer and what to change first. An AI-first SaaS assessment gives you:
- A step-by-step map of one workflow, marked by what to expose to agents, trigger from events, automate, redesign or retain
- The capability and permission changes each layer needs
- The layers that can stay as they are
- A prioritized engineering path for the first release
Assess Your SaaS for an AI-First Rebuild
References
- Gartner. Gartner Predicts 40% of Enterprise Apps Will Feature Task-Specific AI Agents by 2026, Up from Less Than 5% in 2025. Gartner Newsroom. August 2025. https://www.gartner.com/en/newsroom/press-releases/2025-08-26-gartner-predicts-40-percent-of-enterprise-apps-will-feature-task-specific-ai-agents-by-2026-up-from-less-than-5-percent-in-2025
- Gartner. Gartner Predicts Over 40% of Agentic AI Projects Will Be Canceled by End of 2027. Gartner Newsroom. June 2025. https://www.gartner.com/en/newsroom/press-releases/2025-06-25-gartner-predicts-over-40-percent-of-agentic-ai-projects-will-be-canceled-by-end-of-2027
- Forrester. Predictions 2026: AI Agents, Changing Business Models, And Workplace Culture Impact Enterprise Software. Forrester Blogs. 2025. https://www.forrester.com/blogs/predictions-2026-ai-agents-changing-business-models-and-workplace-culture-impact-enterprise-software
- Aleksandra Todorova, Anthropic. How monday.com transformed its platform into an agent-first product where humans and agents collaborate. Claude Blog. August 2026. https://claude.com/blog/how-monday-com-transformed-its-platform-into-an-agent-first-product-where-humans-and-agents-collaborate
- Fin (Intercom). Fin AI Agent Pricing. fin.ai. Accessed October 2026. https://fin.ai/pricing
- OWASP GenAI Security Project. LLM06:2025 Excessive Agency. OWASP Top 10 for LLM Applications 2025. 2025. https://genai.owasp.org/llmrisk/llm062025-excessive-agency/